RockCloud-基石云安全-官方博客
DDoS Attack Log Analysis and Traceback Methods: Layered Forensics and Response When Bandwidth Is Saturated
When a server's bandwidth is saturated or CPU is maxed out, this article provides a layered log-based forensics method to classify the attack type by analyzing inbound traffic characteristics, L4 connection states, and L7 access records, and map them to actionable response actions.
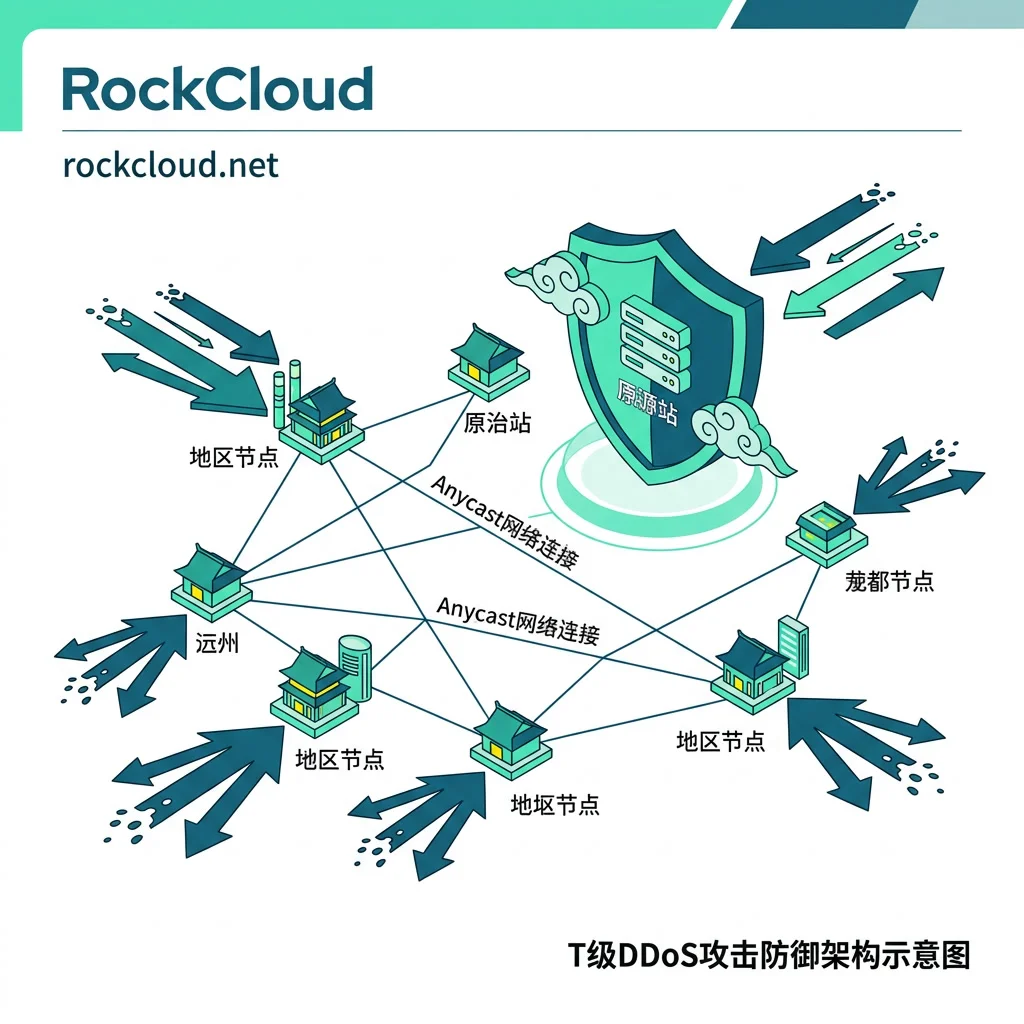
Architecture for Handling Tbps-Scale DDoS Attacks: Single Data Center or Multi-Region Edge Offload?
Handling Tbps-scale DDoS attacks requires distributed edge-based offload across multiple locations; a single data center will break at the upstream link first. This article breaks down the four-layer responsibilities and provides a selection comparison table and a self-check checklist.
High-Protection IP vs High-Protection Server: Cost and Effectiveness Comparison
A detailed cost-benefit analysis comparing high-protection IP and high-protection servers across four key dimensions, with practical recommendations for different business scenarios.
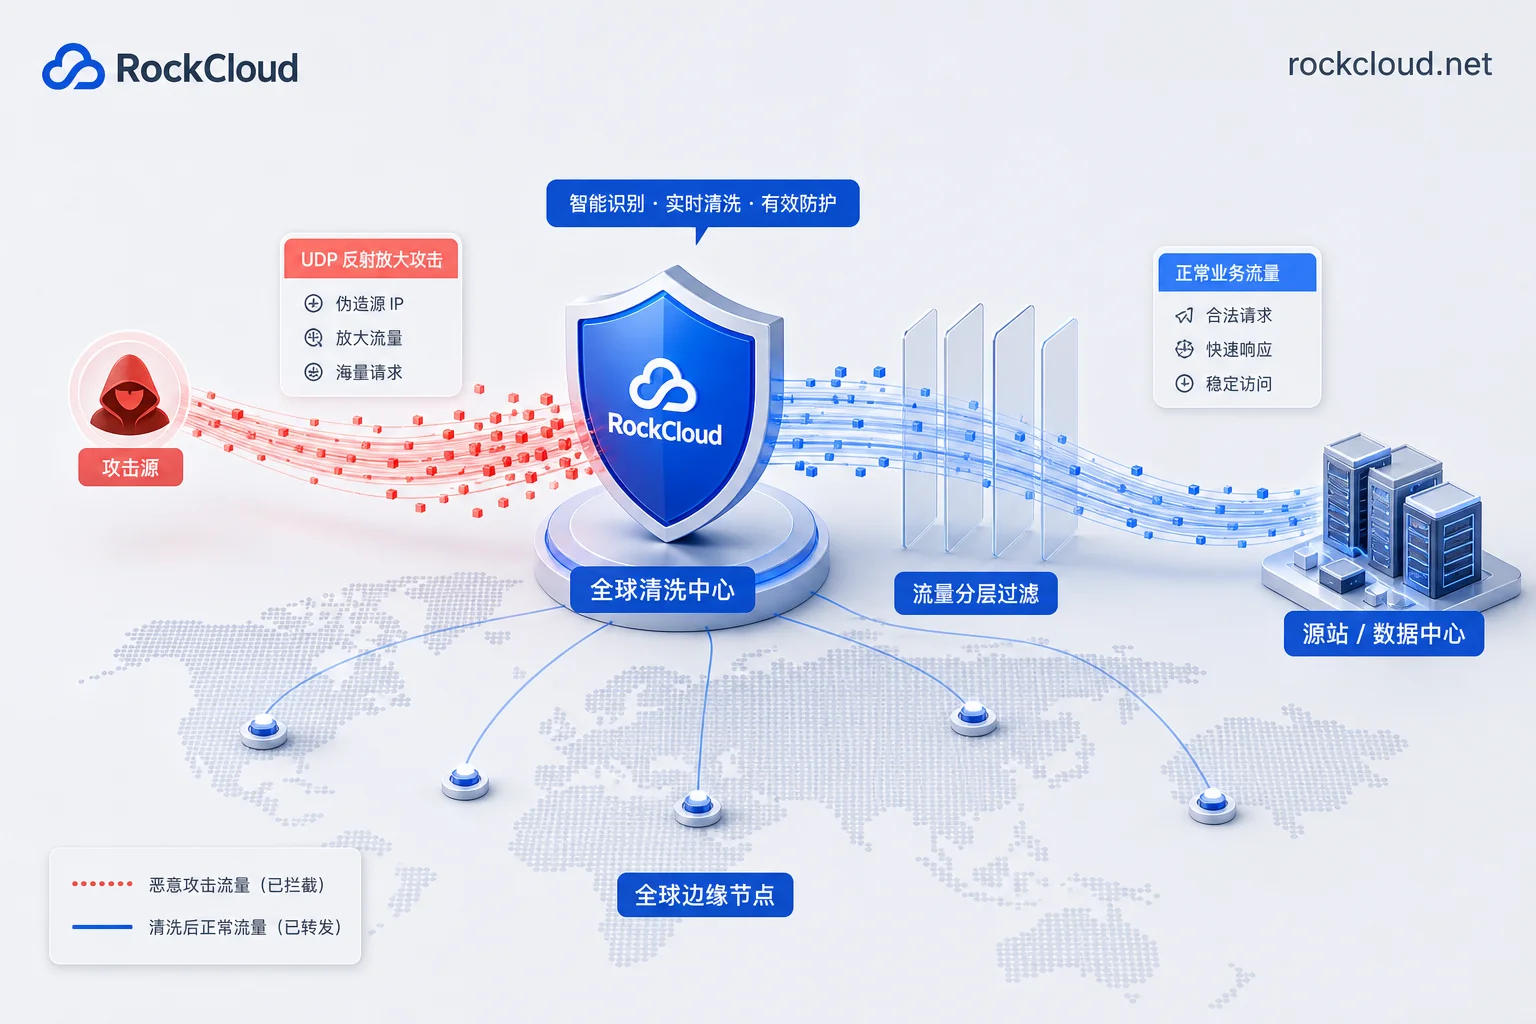
Pros and Cons of Blocking Overseas UDP Traffic on Overseas High-Defense IP: How to Decide Among 4 Trade-offs
Blocking overseas UDP traffic on overseas high-defense IP can quickly stop reflection amplification attacks, but it also disrupts DNS, QUIC, gaming protocols, and more. This article breaks down the pros and cons and offers four strategic trade-offs.
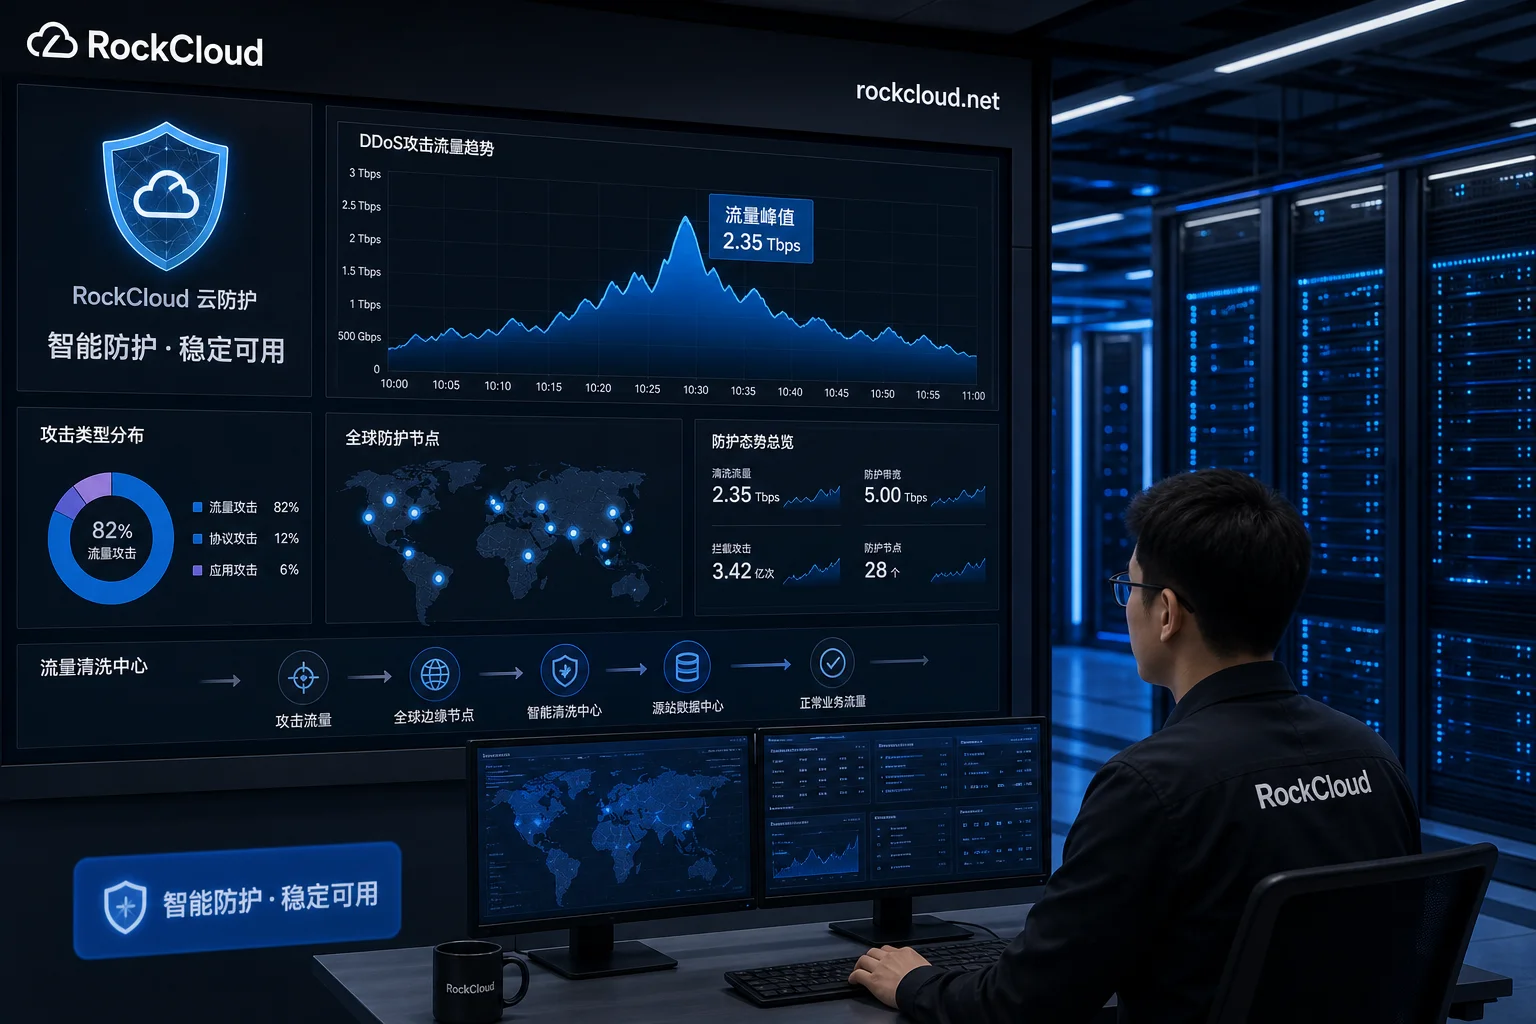
Dedicated vs. Shared High-Protection IPs: Four Key Differences Explained
Dedicated and shared high-protection IPs differ mainly in bandwidth exclusivity, blackhole fault domain, IP reputation, and peak handling authority. This article details these four differences, backed by NETSCOUT's report on ultra-large-scale floods, and provides verification questions and red flags for pre-contract checks, along with selection guidance by business type.