RockCloud-基石云安全-官方博客
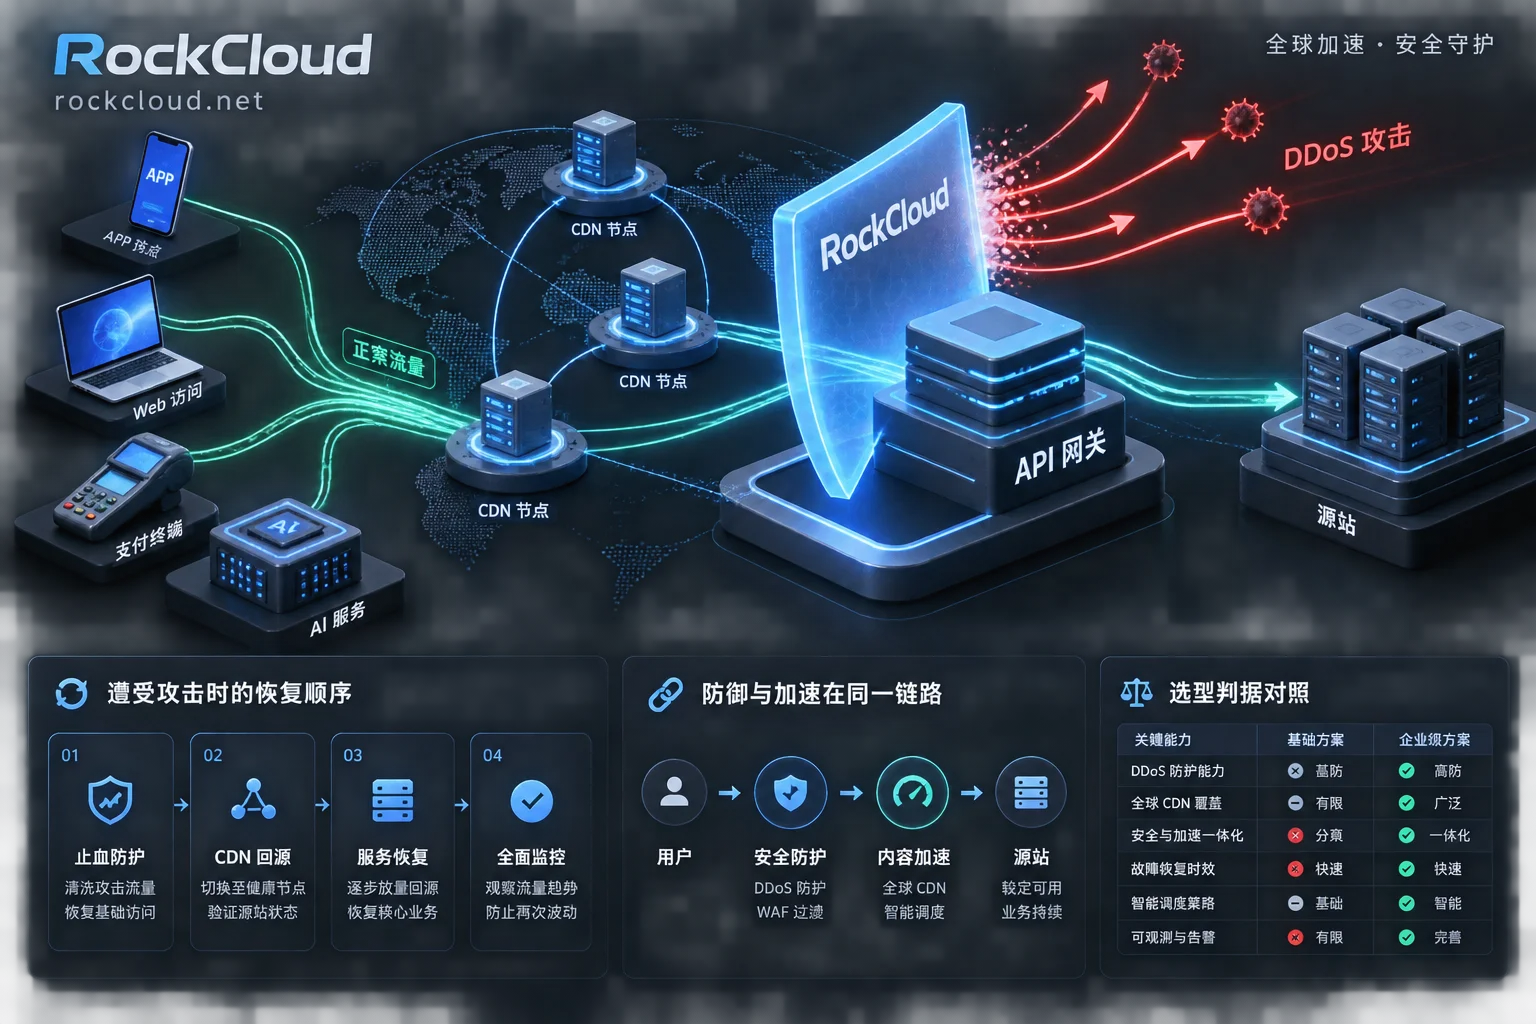
How to Implement API DDoS Protection: Architecture for Mitigating Multi-Vector Attacks Without Blocking Legitimate Clients
This article addresses API services such as app backends, payment gateways, and AI model interfaces, analyzing the characteristics of multi-vector DDoS attacks combining Layer 4 traffic floods and Layer 7 concurrency. It explores how to implement API DDoS protection without affecting legitimate clients and callback notifications, using Anycast scrubbing, intelligent WAF exception rules, TLS 1.3 0-RTT acceleration, and fixed peak billing architecture.
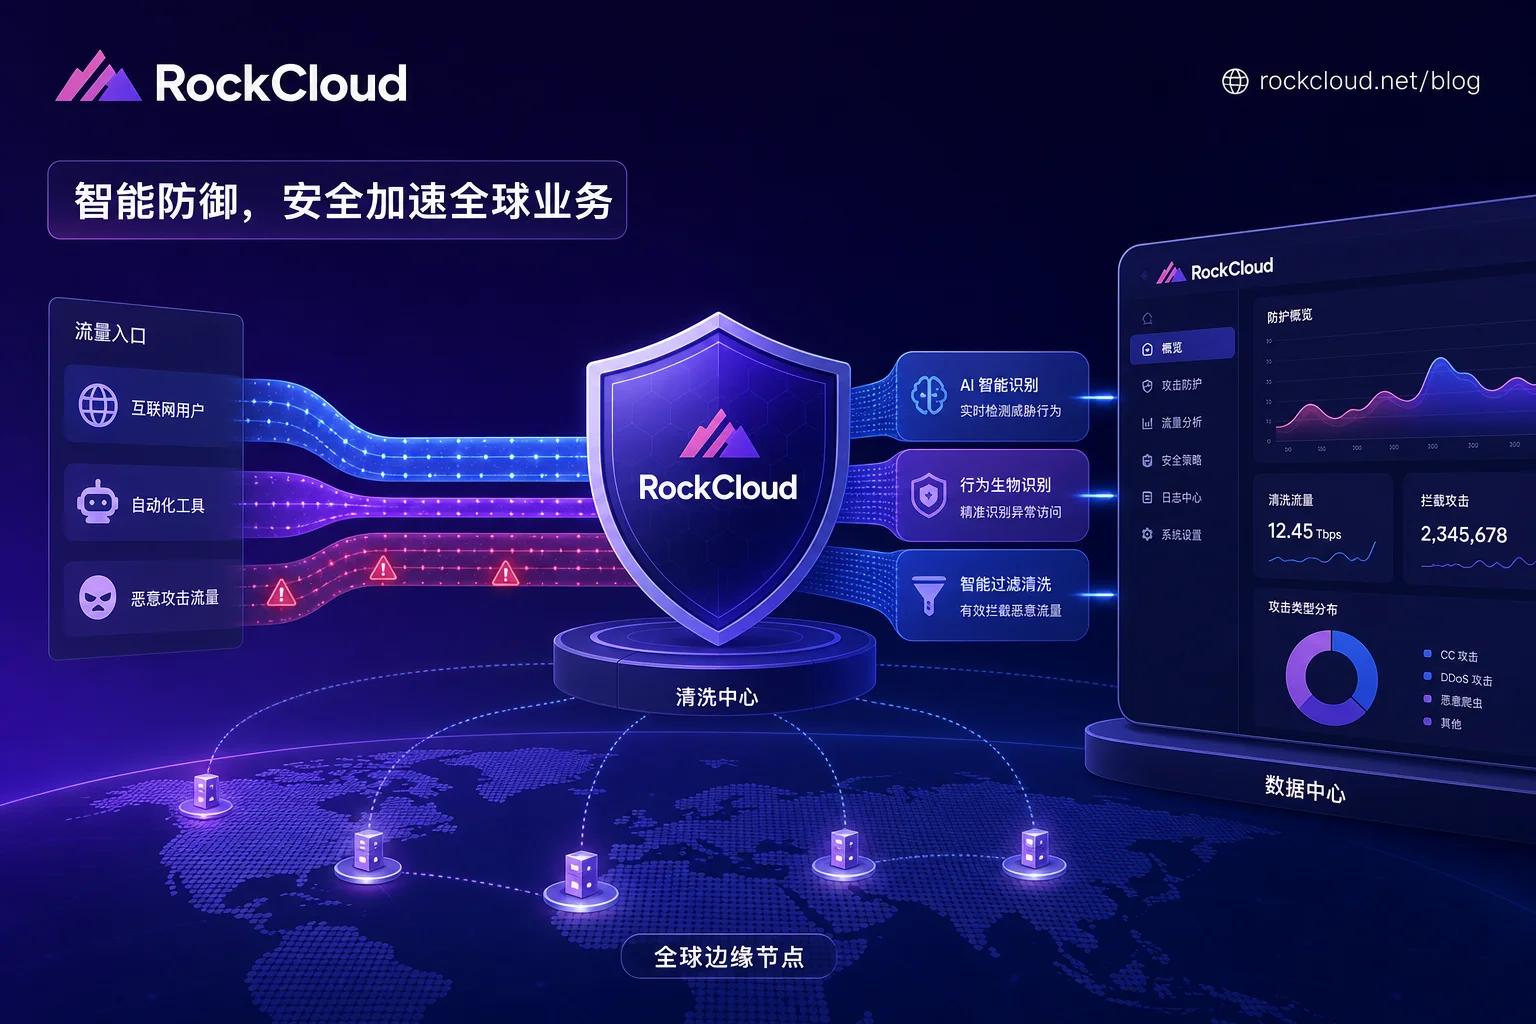
Bot Management in the Age of AI Agents: Interpreting Enterprise Automation Threats and Selecting Defense Architectures
As AI agents reshape internet traffic, enterprises must evolve from basic crawler defense to sophisticated bot management, leveraging edge solutions like RockCloud for comprehensive protection.
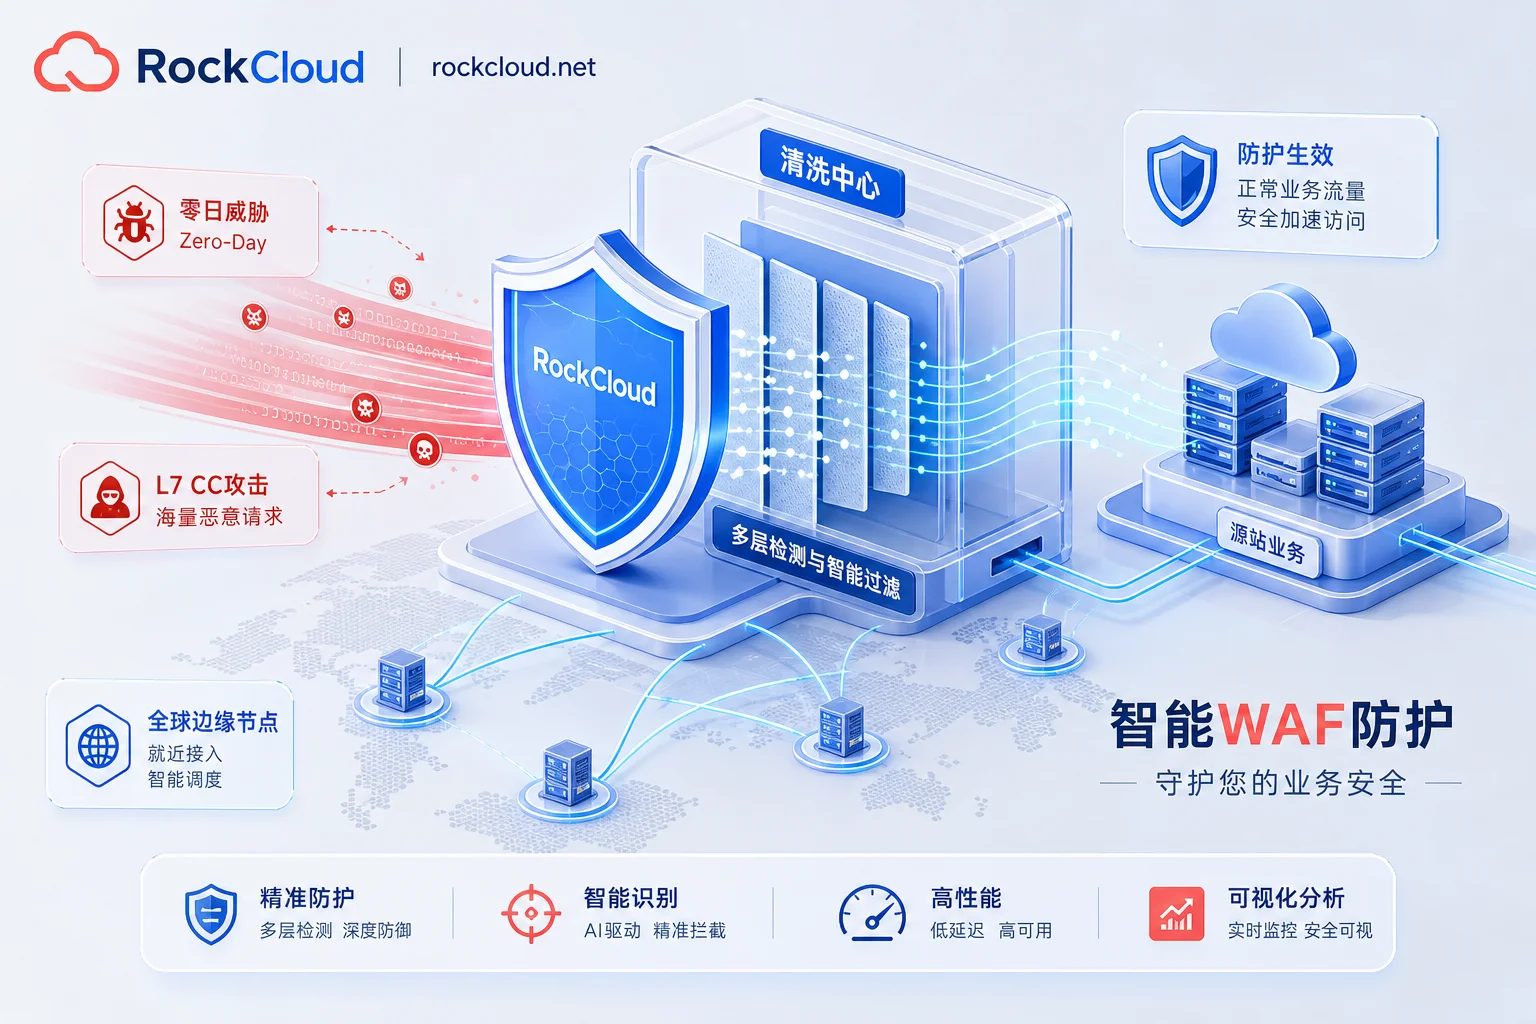
2026 Surge in Web Application Attacks: How Enterprises Can Reshape Intelligent WAF Protection Amid High-Risk 0day Exposures?
In 2026, web application attacks are surging, with high-risk 0day vulnerabilities being quickly exploited; enterprises must upgrade to intelligent WAF solutions that incorporate edge virtual patching, AI behavioral analysis, and CDN integration.
Practical Guide to Application-Layer Attack Defense: How Enterprises Can Restructure L7 Protection Against Realistic Bots and API Surge
Enterprises must adopt layered defense, including edge filtering, behavioral WAF, and source hiding, to counter sophisticated L7 attacks like high-fidelity bots and API abuse.
2026 API DDoS Protection Guide: Layered Defense Against L7 Traffic Surges and Business Logic Abuse
This guide explores modern layered defense strategies for API DDoS protection, including edge scrubbing, business logic validation, and dynamic rate limiting, with practical insights for guarding against L7 attacks.