RockCloud-基石云安全-官方博客
DDoS Attack Incoming: Don't Let Your Business Crash While 'Waiting for Response' — RockCloud Emergency Response Manual
When your business suffers a sudden DDoS attack, every second lost means lost users and revenue. This article summarizes an emergency avoidance guide during an attack and explores how RockCloud's high-defense CDN enables 'minute-level' rapid onboarding, hiding the origin server while integrating defense and acceleration to help your business run smoothly through the storm.
Bot Management: How to Use Edge WAF for Fine-Grained Traffic Control When AI Crawlers and Automated Scripts Flood Login and Payment APIs
In 2026, malicious bot traffic is growing more than 9 times faster than human traffic, and attacks are shifting from public page scraping to core business flows like login, shopping cart, and payment. This article combines the latest industry security reports to analyze why traditional static anti-scraping rules fail and shares how to implement an efficient bot management architecture using high-defense CDN, intelligent WAF machine learning, and custom rules from security teams.
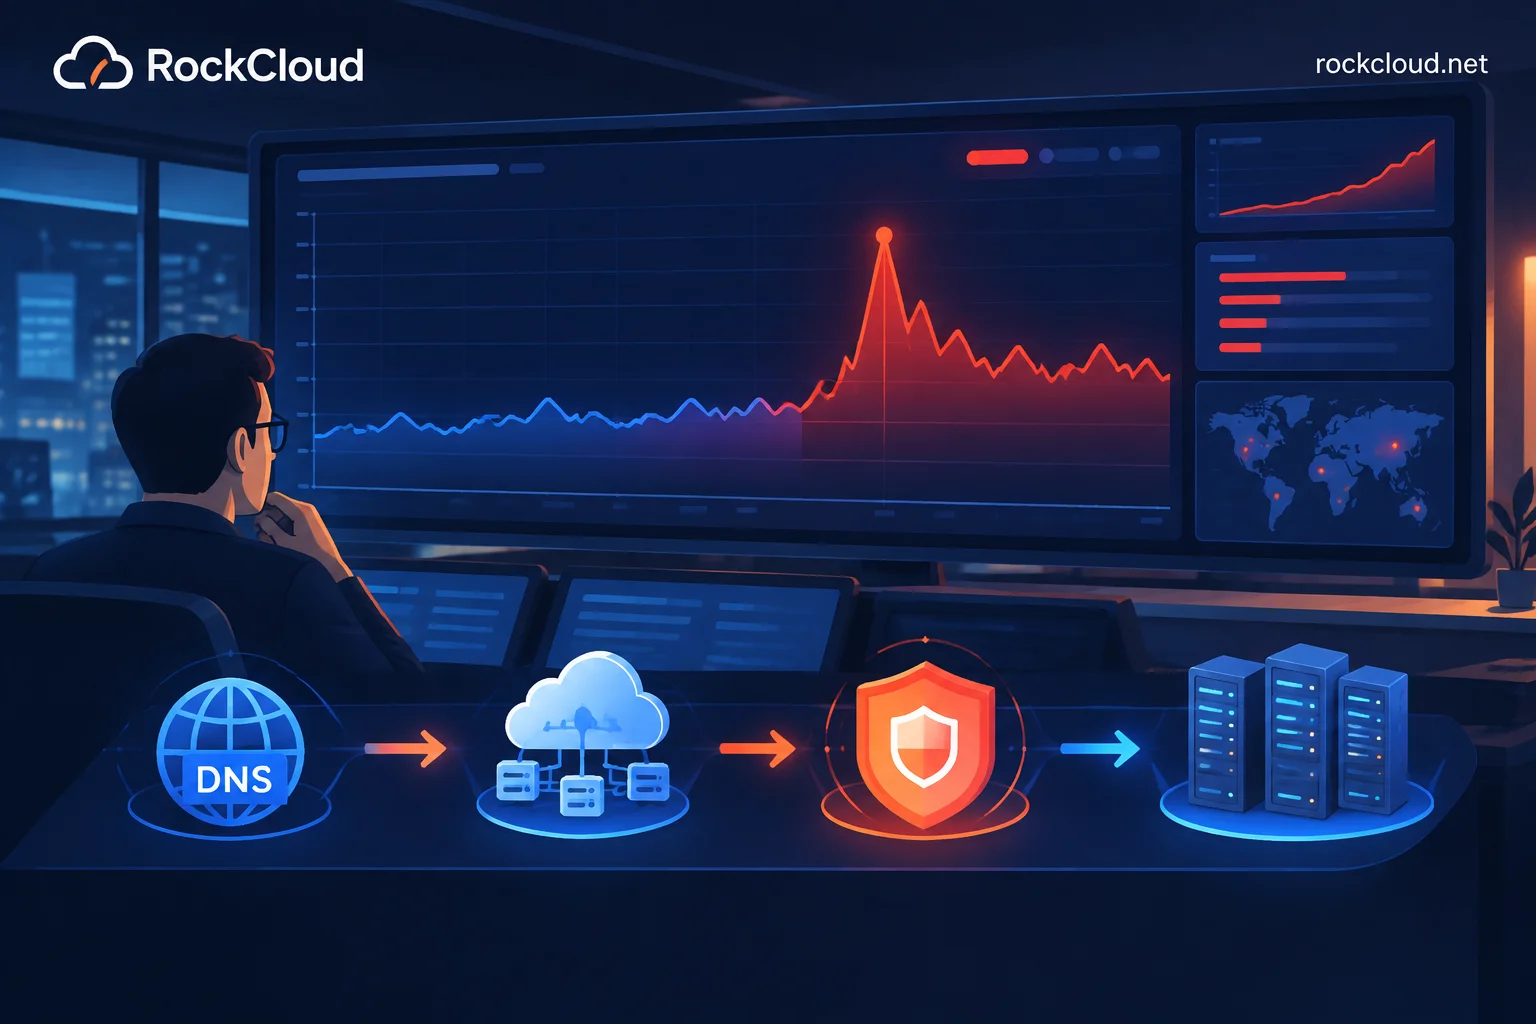
Your Website Is Under a Large-Scale Attack: Fast CDN Onboarding Order and Lockdown Essentials
When an attack is already underway, mounting a CDN isn't just about registering an account. This article lays out the actual hands-on order: configure origin pull and certificates on the CDN side, verify the path with hosts, then switch DNS, then lock down the origin firewall or change IPs, and finally enable edge emergency mode—plus handling exceptions like TTL caching, API services that can't go through challenges, and an origin that's already been blackholed.
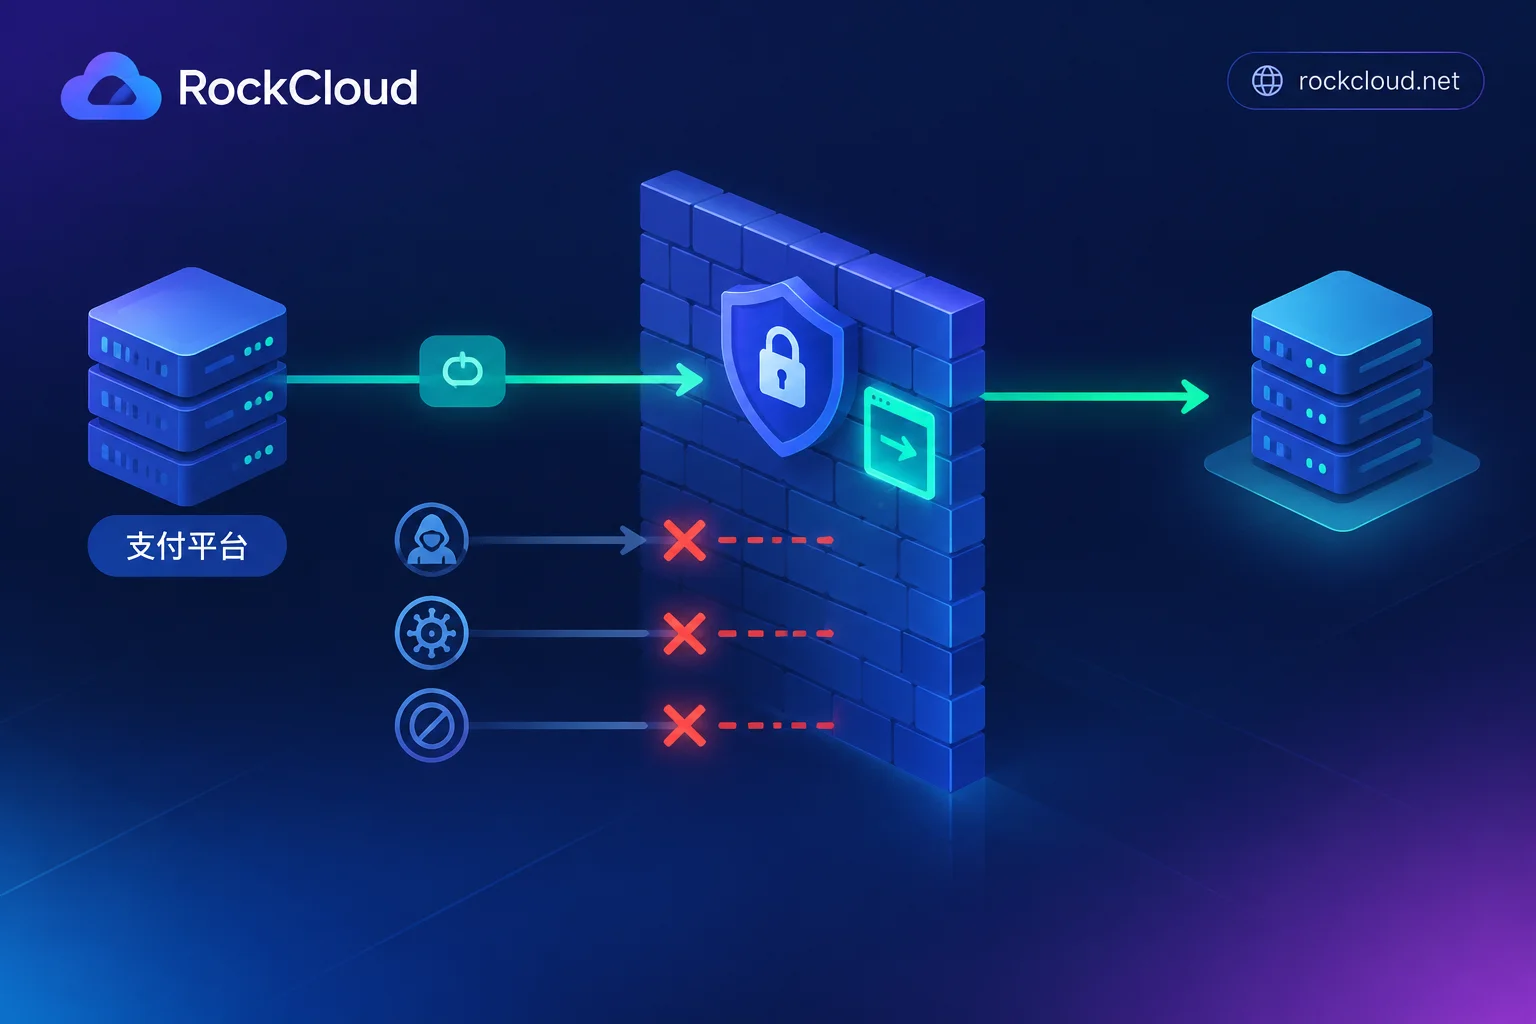
WAF Blocked Your Payment Callback? How to Whitelist: Check Rule ID First, Then Add IP Precise Allow by Path
Payment succeeds but orders don't update, and the payment platform reports notification failure—most likely the WAF treated the callback request as an attack. This article provides the recovery order: first locate the blocking module and rule ID in the interception logs, then use a combination of 'POST + callback path + payment platform official IP range' to allow only that endpoint and only skip the hit module, finally resend the notification to verify, and retain business-layer signature verification.
How to Prevent Real Origin IP Exposure: 5 Leak Points to Self-Check and Origin Closures
A practical checklist to identify and close origin IP leaks, and lock down access to ensure CDN protection isn't bypassed.