RockCloud-基石云安全-官方博客
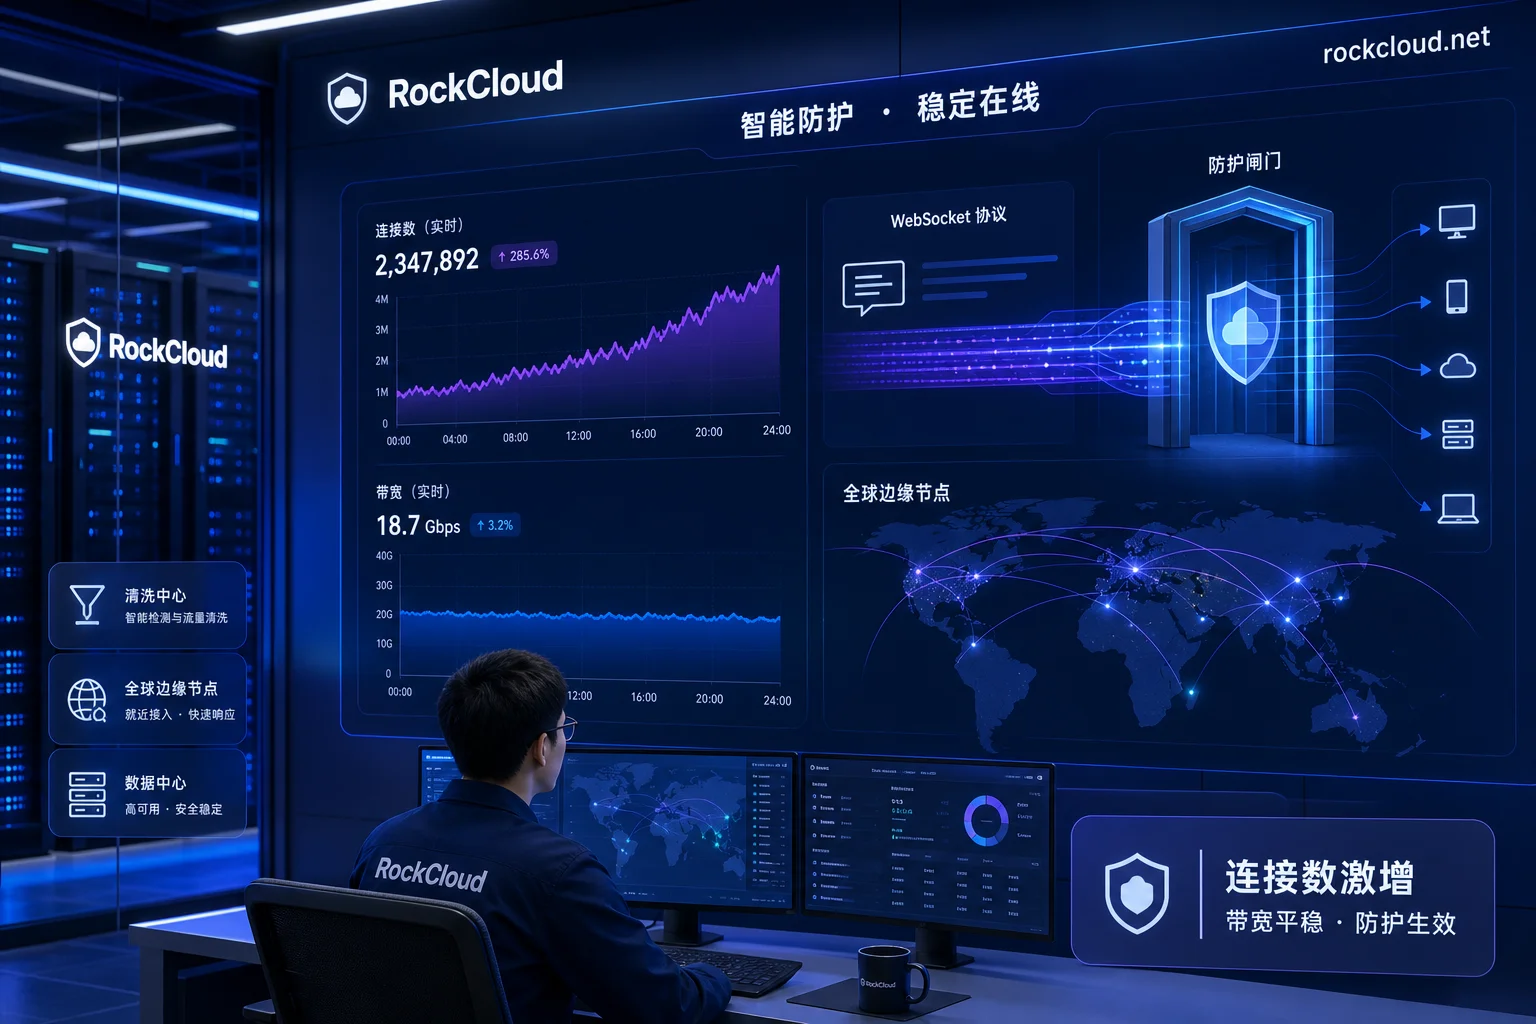
WebSocket Long-Connection DDoS Attack Defense: Four-Gate Configuration
Defending against WebSocket long-connection DDoS attacks hinges on four gates: handshake authentication, per-IP concurrent connection quotas, message rate limiting, and idle heartbeat timeout reclamation, as traditional WAFs lose inspection after the HTTP 101 upgrade.

Dynamic CAPTCHA in Anti-CC Attack: Which Paths Trigger and What Thresholds
Effective dynamic CAPTCHA in anti-CC requires tiered triggering based on path value, using transparent checks, silent JS challenges, and interactive CAPTCHAs, adjusted automatically by anomaly signals, deployed at the edge, and clearly bounded by rate limiting and edge scrubbing.

How to Choose High-Protection CDN? Six Criteria to Self-Test Before Signing
Learn the six key criteria to evaluate high-protection CDN providers before signing, beyond nominal defense peaks.

BGP High-Protection vs Single-Line High-Protection: Differences and Selection Guide for Enterprise Quotation Comparison
Understand the key differences between BGP and single-line DDoS protection, focusing on routing control and mitigation authority, with a practical comparison table and selection checklist.
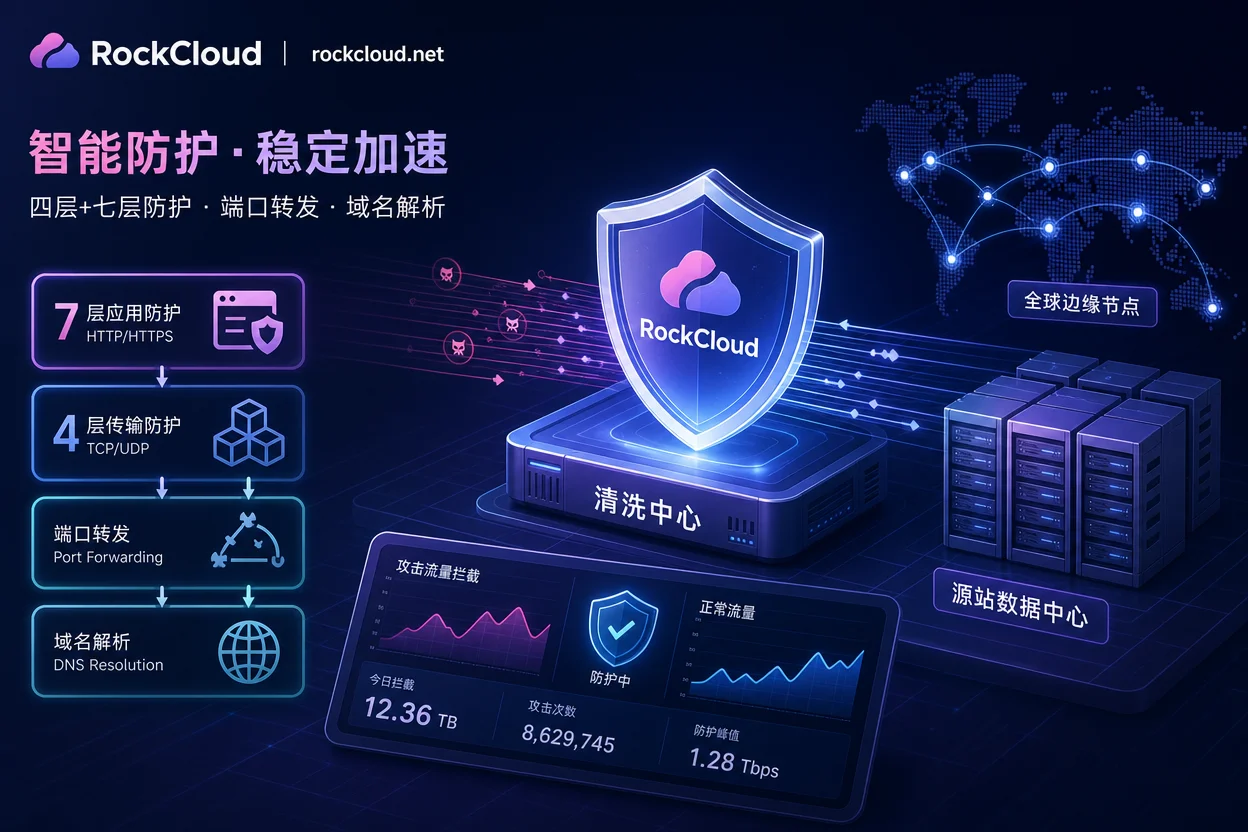
High-Protection IP vs. High-Protection CDN: Key Differences and Selection Guide for Enterprises
Understand the core differences between high-protection IP and high-protection CDN, including protocol layers, capabilities, and selection criteria for modern DDoS threats.