RockCloud-基石云安全-官方博客
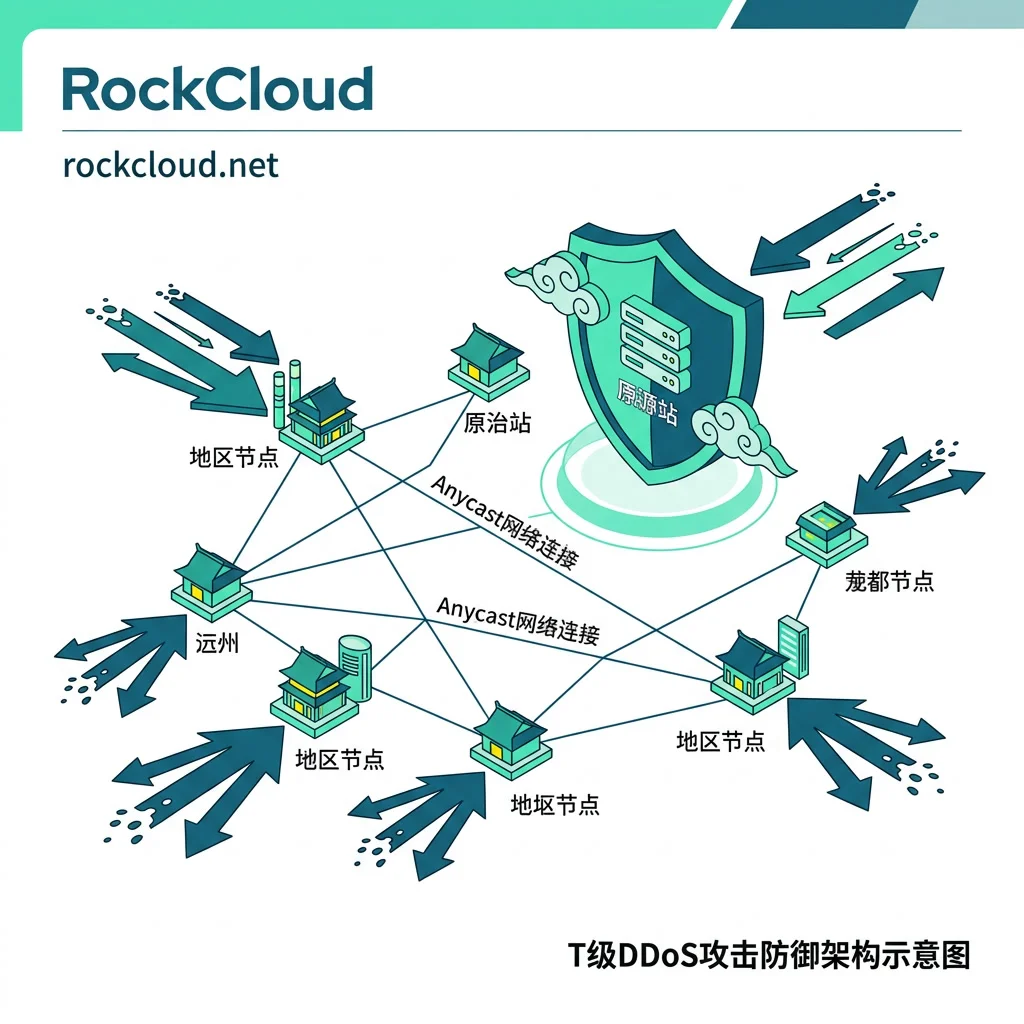
Architecture for Handling Tbps-Scale DDoS Attacks: Single Data Center or Multi-Region Edge Offload?
Handling Tbps-scale DDoS attacks requires distributed edge-based offload across multiple locations; a single data center will break at the upstream link first. This article breaks down the four-layer responsibilities and provides a selection comparison table and a self-check checklist.
How to Prevent Real Origin IP Exposure: 5 Leak Points to Self-Check and Origin Closures
A practical checklist to identify and close origin IP leaks, and lock down access to ensure CDN protection isn't bypassed.
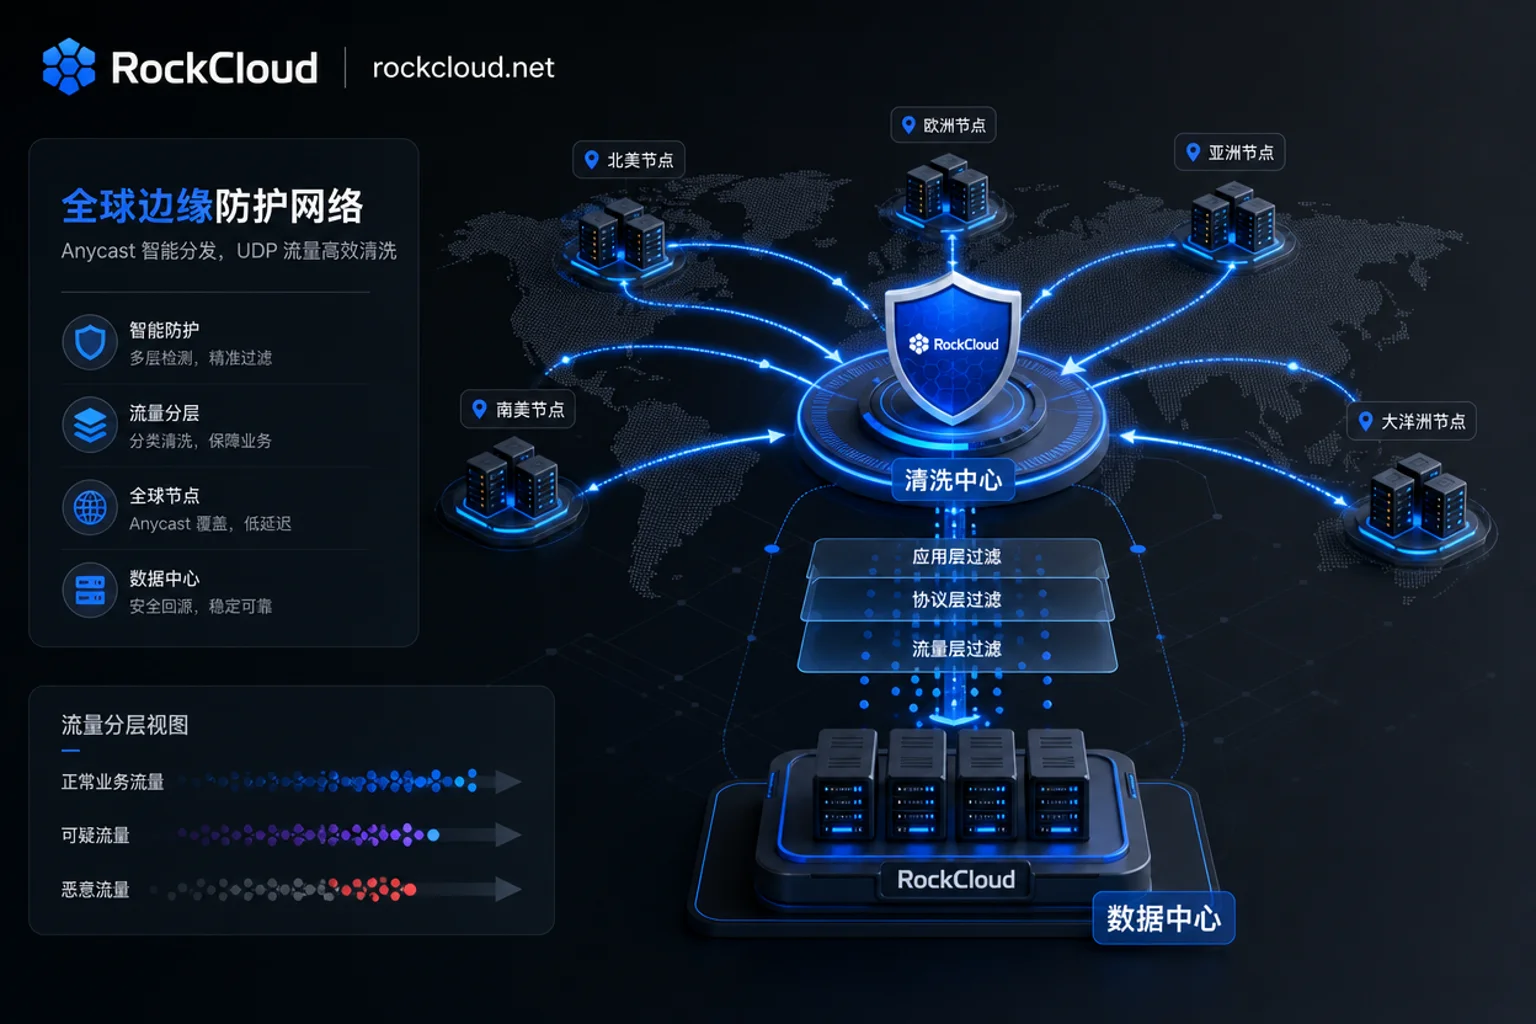
NTP Reflection Amplification Attack Principles and Defense: Shut Down Amplifiers in 4 Steps
Learn how to mitigate NTP reflection amplification attacks by understanding the amplification mechanism, identifying whether you are a victim or a reflector, closing the monlist vulnerability, and moving traffic scrubbing to the network edge.
How to Handle DDoS Emergency Response? The Order of Operations Before and After Blackholing
A time-based 4-step DDoS emergency response playbook, covering attack confirmation, traffic diversion, blackhole handling, and post-recovery review, with practical checklists.
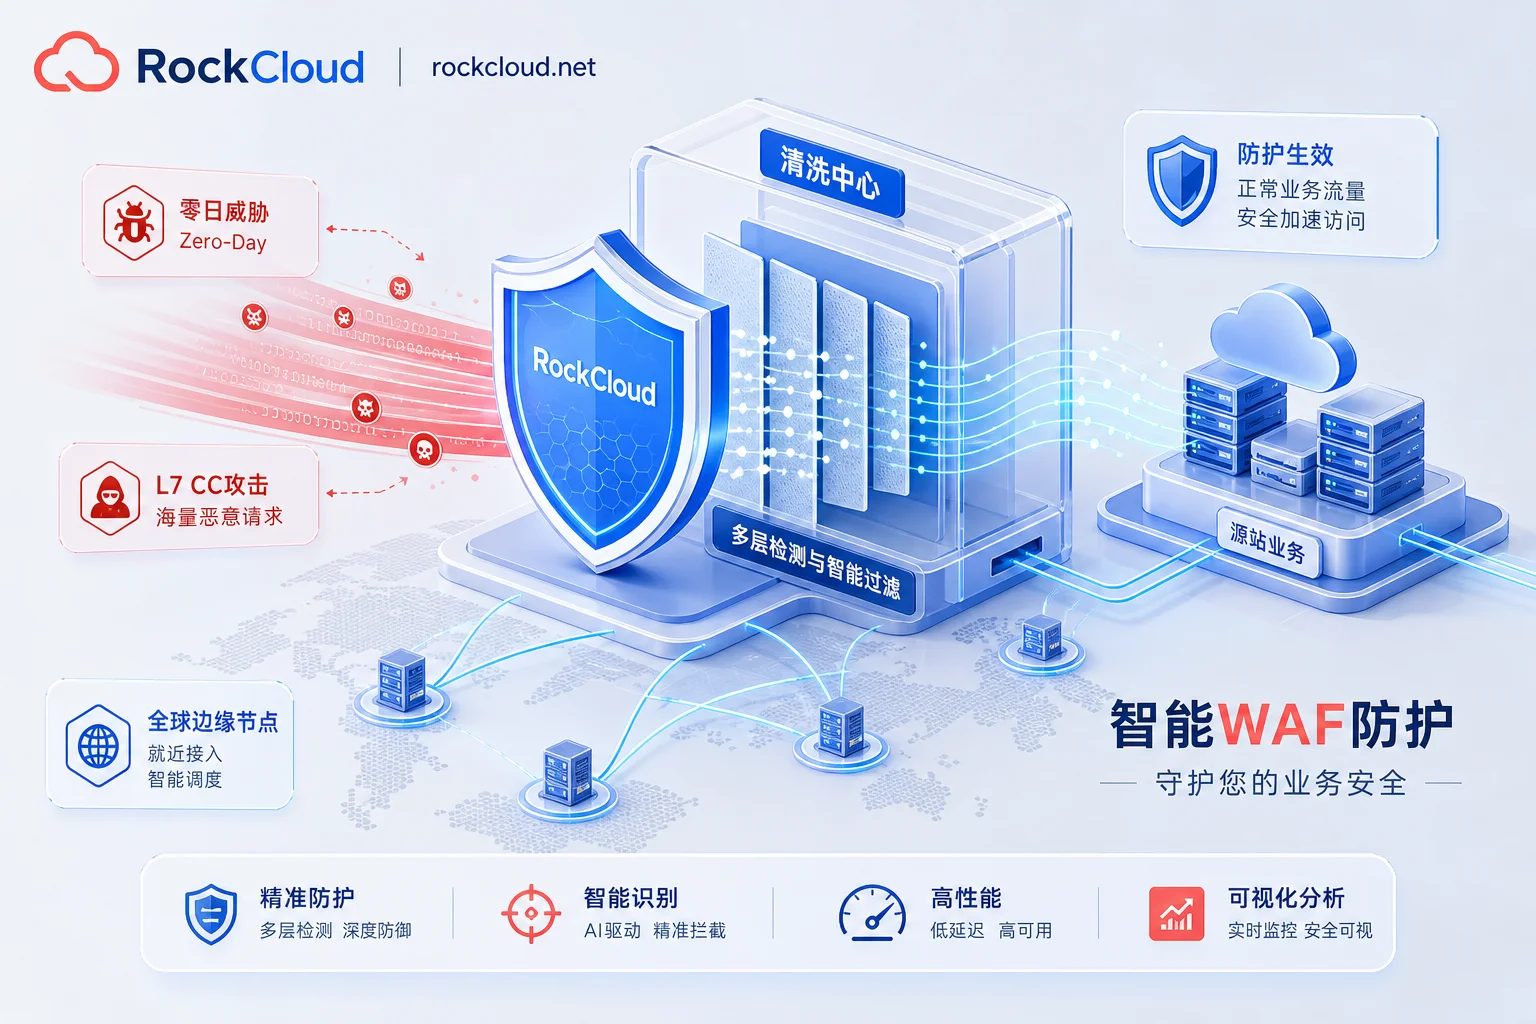
2026 Surge in Web Application Attacks: How Enterprises Can Reshape Intelligent WAF Protection Amid High-Risk 0day Exposures?
In 2026, web application attacks are surging, with high-risk 0day vulnerabilities being quickly exploited; enterprises must upgrade to intelligent WAF solutions that incorporate edge virtual patching, AI behavioral analysis, and CDN integration.