RockCloud-基石云安全-官方博客
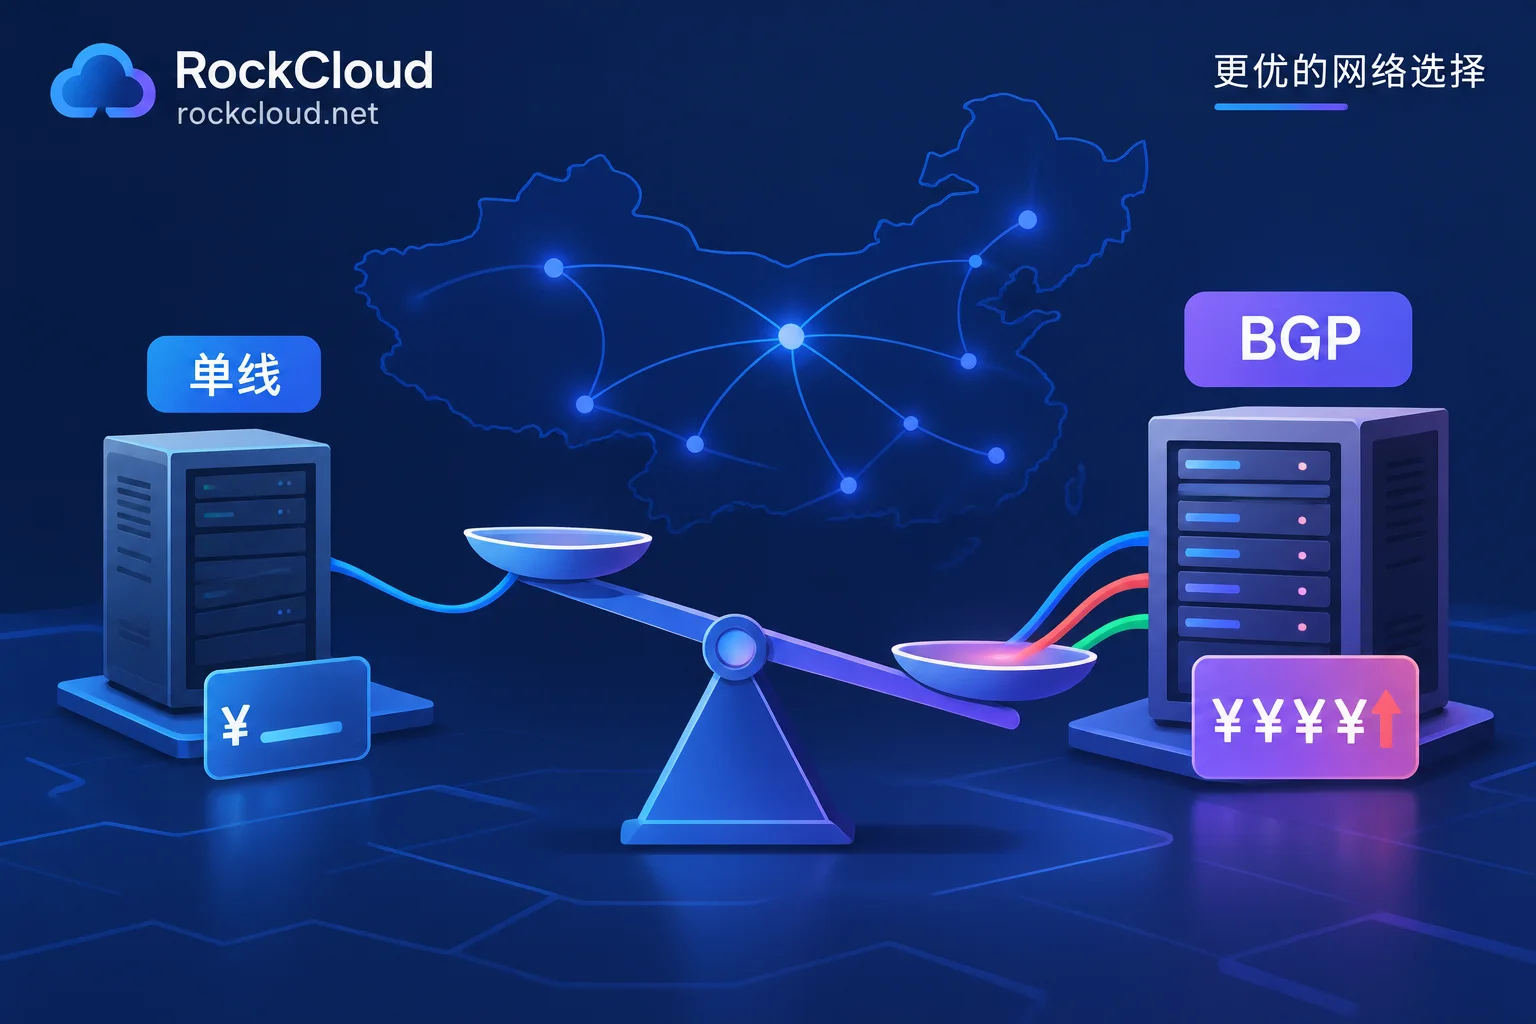
Why Single-Line High-Defense Is Much Cheaper: What You Save on Multi-Line Bandwidth and Cross-Network Redundancy, and Who Pays the Price
Single-line high-defense is cheap mainly because it buys bandwidth from one carrier and skips BGP multi-line routing and redundancy; the savings become cross-network latency for off-network users, who may even be unable to connect during attacks.
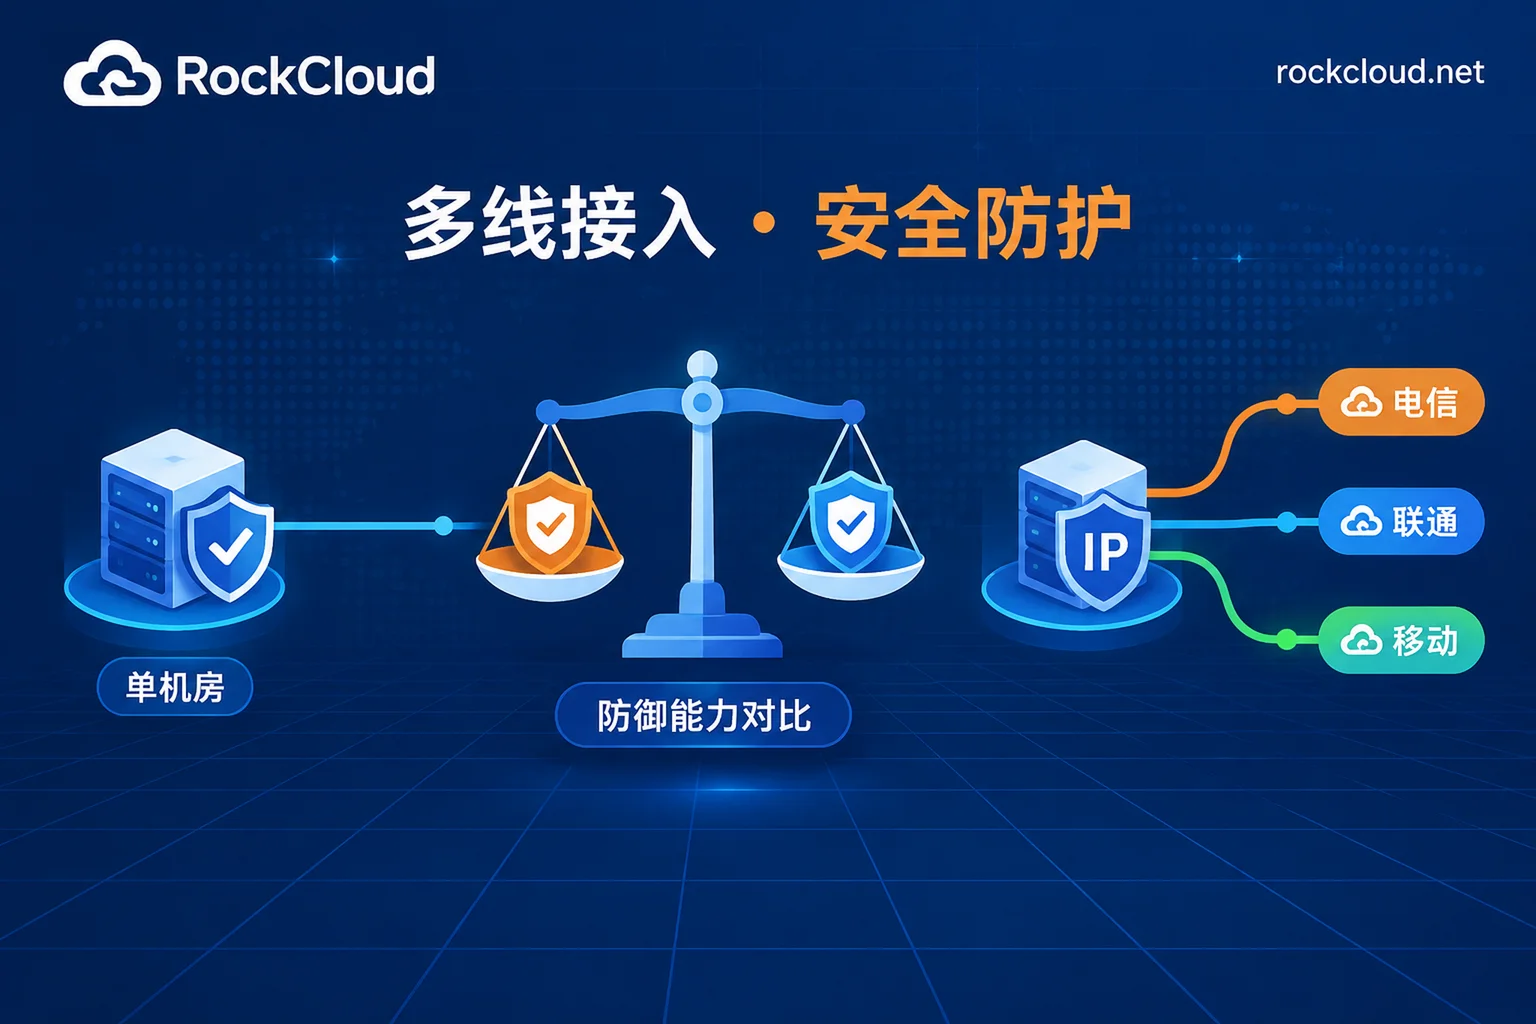
BGP High-Defense vs Single-Line High-Defense: Which Is Stronger — Look at Scrubbing Capacity and Whether Users Can Still Access During an Attack
Paper defense peaks are often higher and cheaper on single-line high-defense, but when users are spread across different carriers, BGP high-defense better preserves nationwide access during an attack. This article breaks down "defense capability" into three criteria, gives business-based selection conclusions, and lists what to ask and test during procurement and testing.
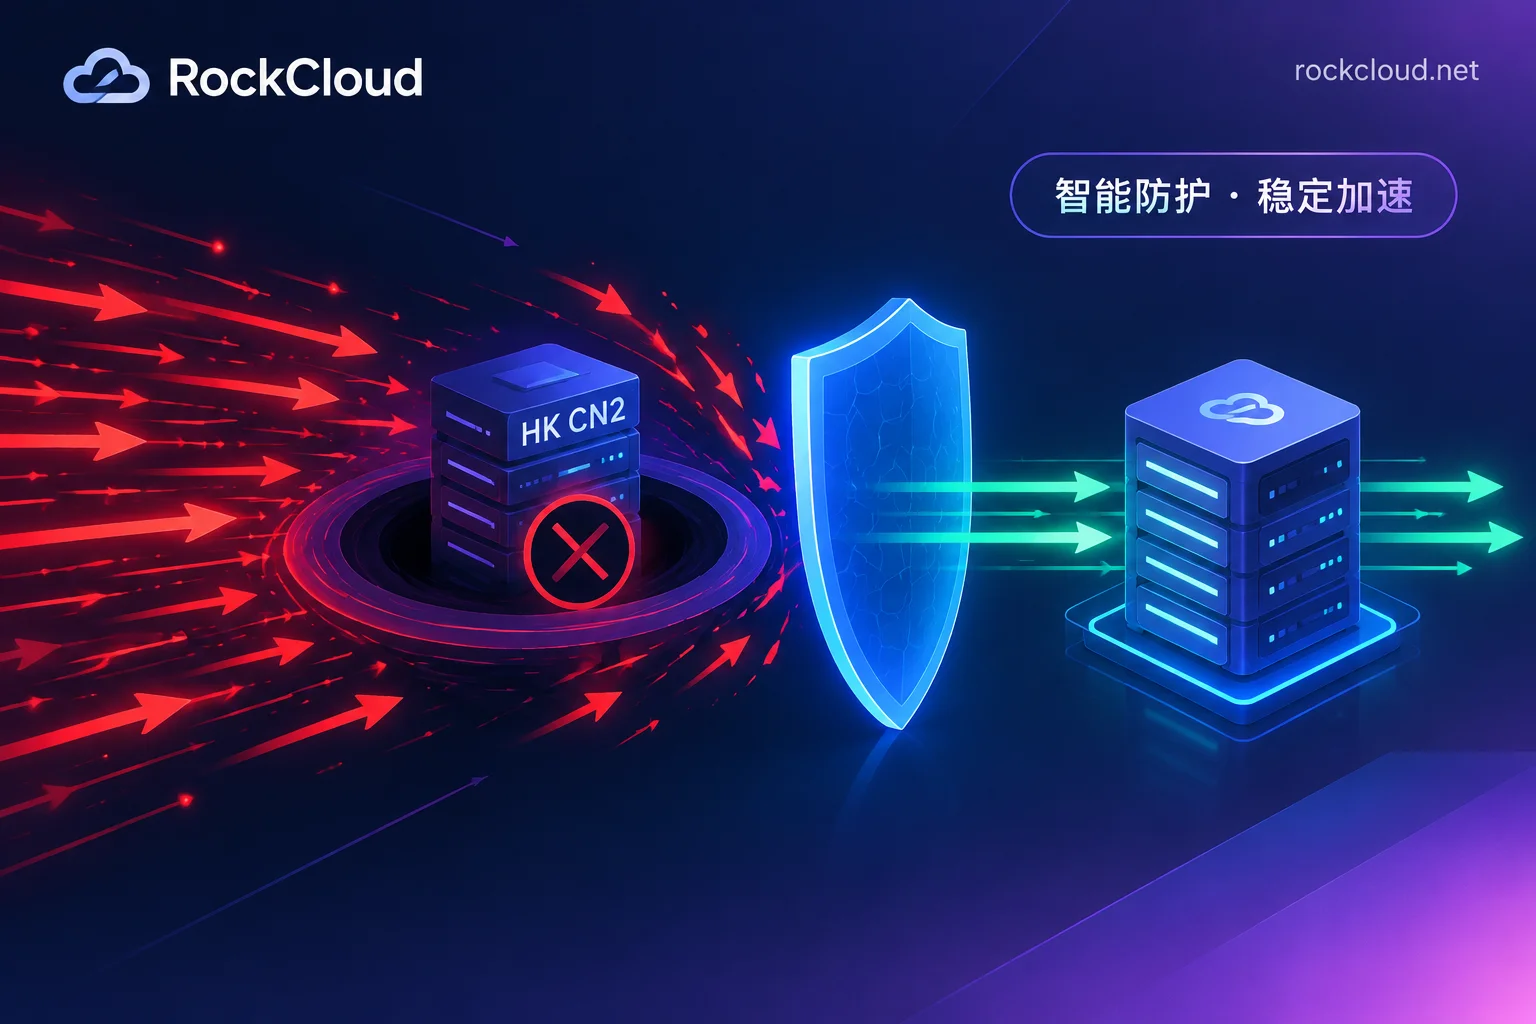
What to Do When a Hong Kong CN2 Server Is Hit by DDoS: Confirm Blackhole, Switch IP, Add Protection, Then Lock Down the Origin
Recovery sequence after a Hong Kong CN2 server is knocked offline by DDoS: check if it's in blackhole, decide whether to wait or change IP, add high-defense based on protocol, allow only origin-pull subnets at the origin, and finally audit IP leaks.
Do You Need High-Protection for Hong Kong Servers? Assess Attack Risk First, Then Choose Your Defense Architecture Based on Business Protocol
Most Hong Kong servers don't need high-protection models directly. This article explains the blackhole risk after an attack on a regular Hong Kong server, then provides more cost-effective and resilient defense architectures for websites/APIs, games and private protocols, and legacy systems, along with conditions to confirm before deployment.
Will the Origin IP Still Be Exposed After Enabling a High-Defense CDN? Five Leak Paths, Hardening Order, and Post-Exposure Response
Even after enabling a high-defense CDN, the origin IP can still leak via historical DNS records, subdomains, email, certificate scans, and application outbound connections. This article provides self-check methods for each leak path, explains the hardening order such as origin whitelisting and default site blocking, and clarifies why you should plug the leaks first and then change the IP when the origin is under direct attack.